If you don't catch it, nobody does.
You're the one who gets asked why email is down, and the only one who'd notice a vulnerability in your stack being exploited today. ThreatLoops answers both before the first ticket lands — 125 live status feeds and the CVE firehose, filtered to the stack you actually run.
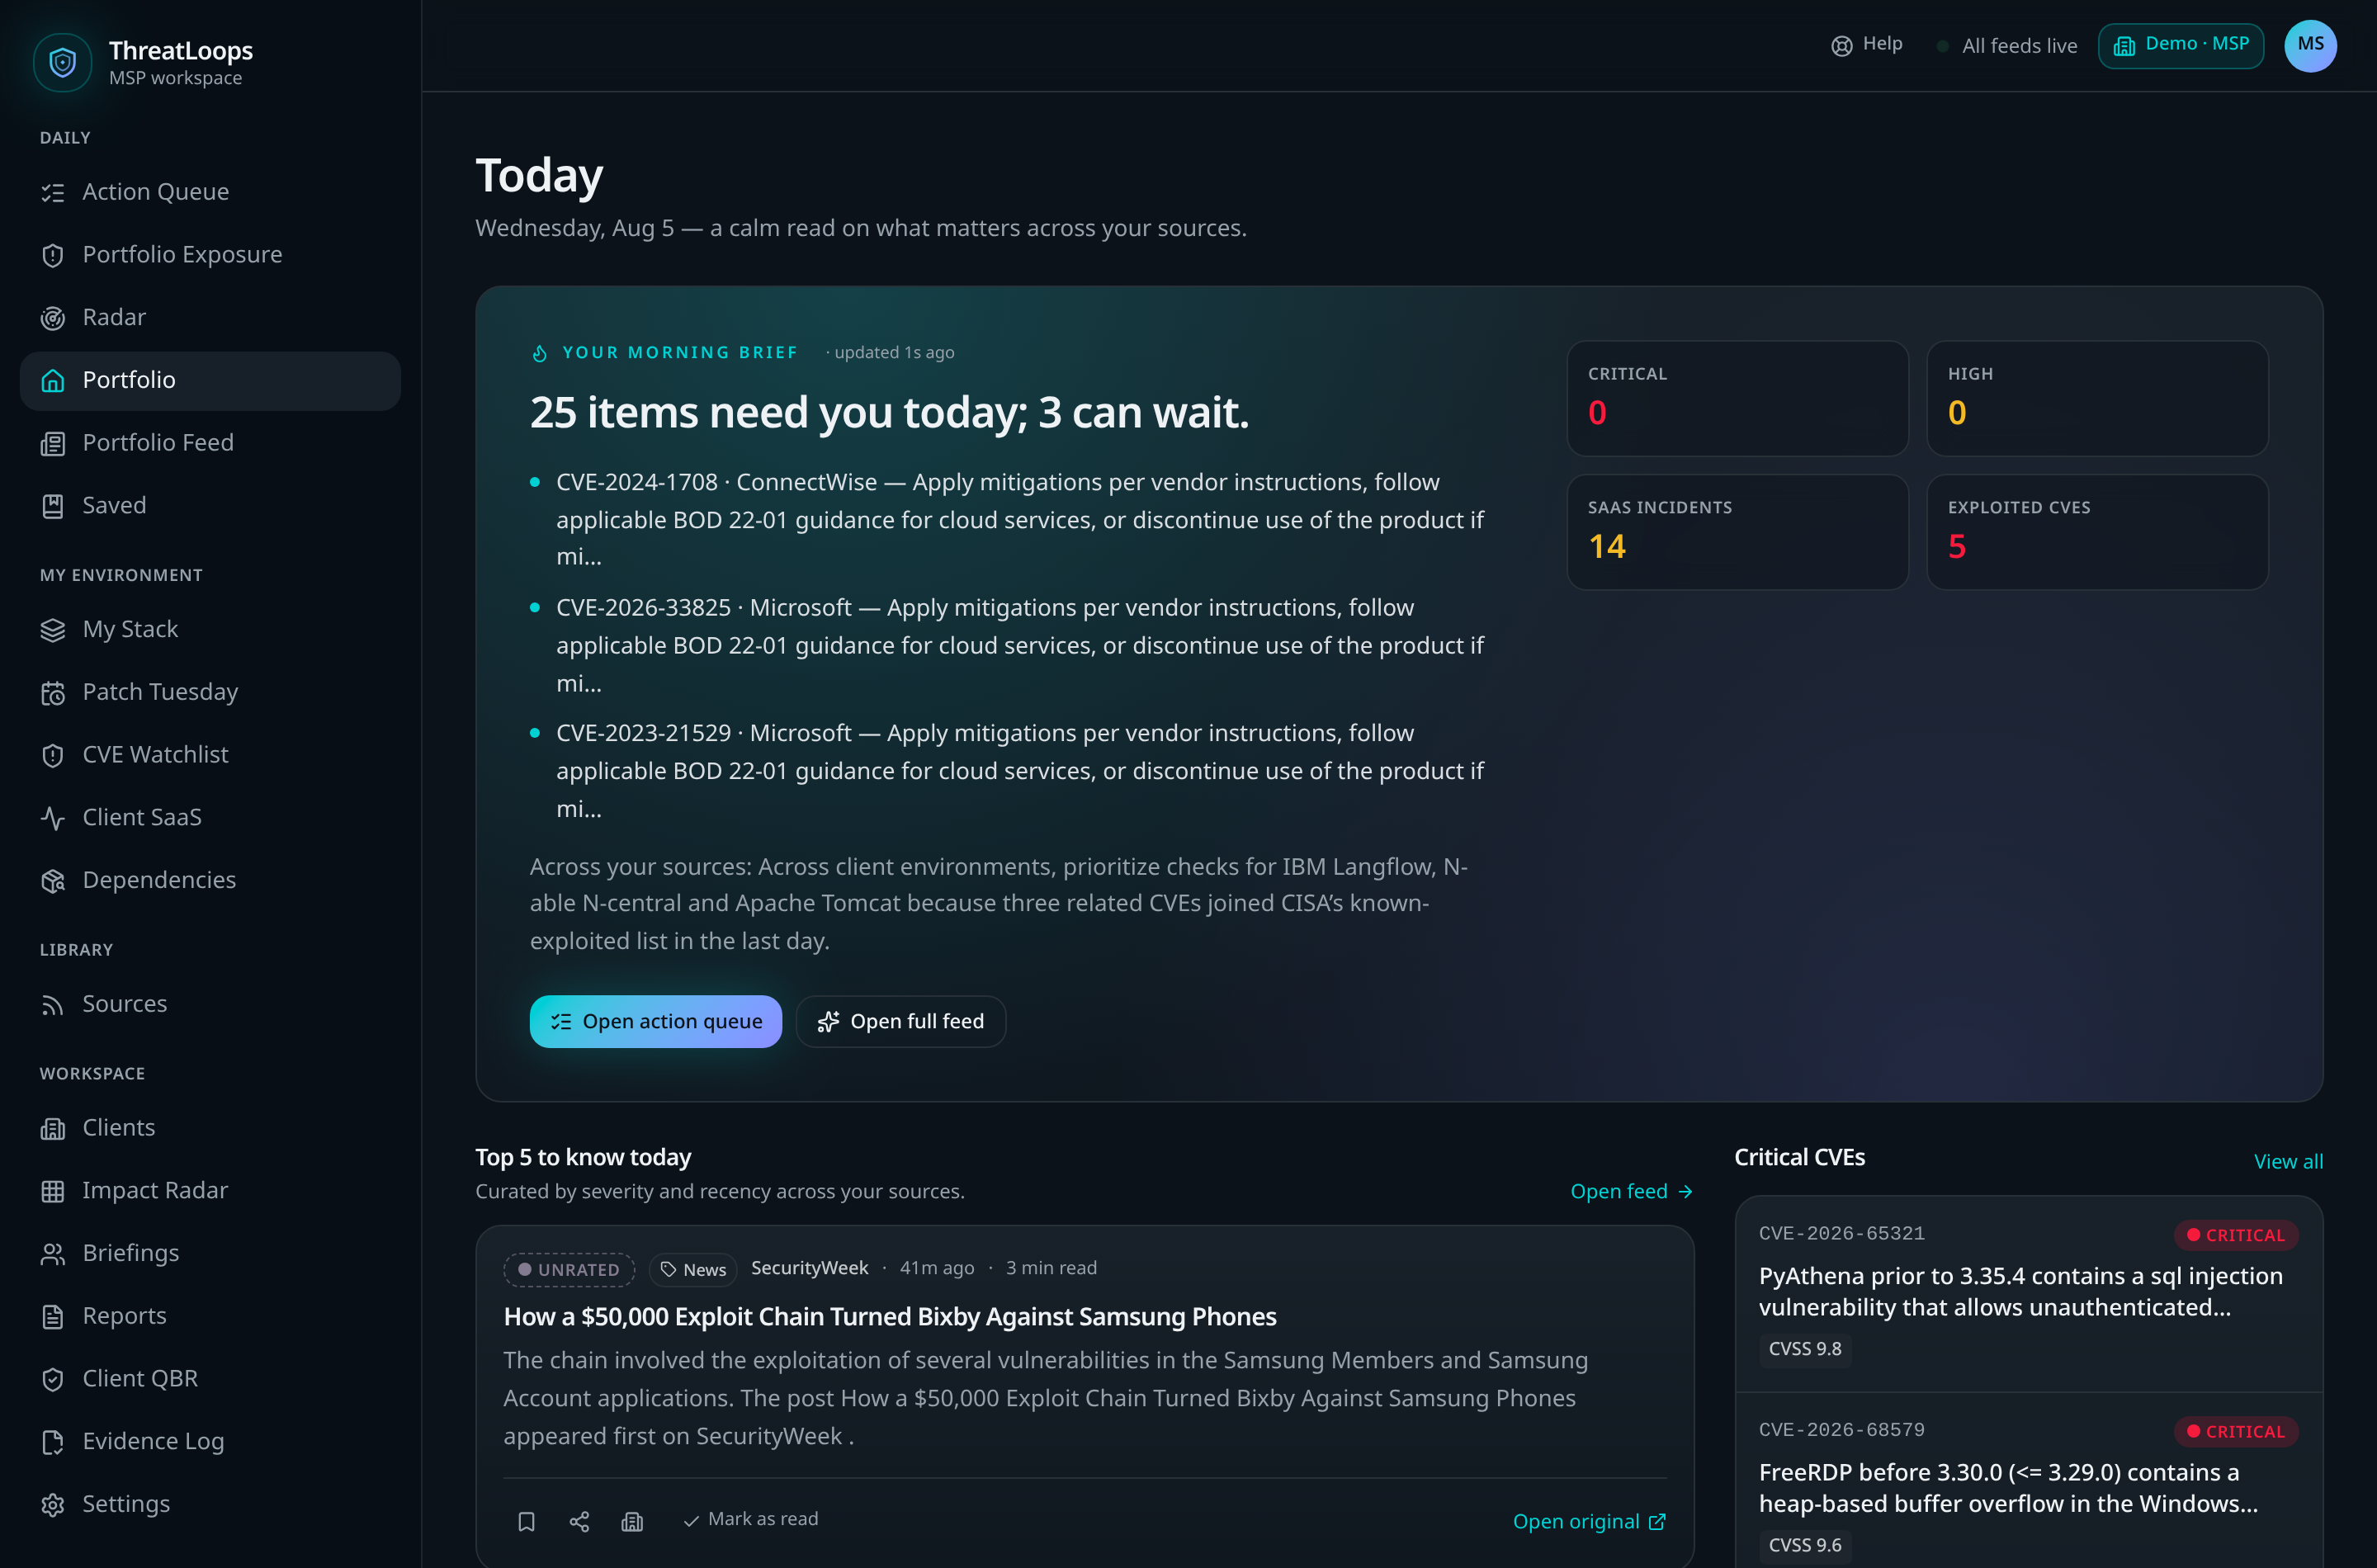
You are the security team, the help desk and the change board.
Nobody else in the building would notice a vulnerability in your stack being actively exploited, and nobody else gets asked why email is slow. ThreatLoops gives you one screen that answers both before the first ticket lands.
"If I don't see it, nobody sees it."
Open the demo in this mode- Full threat feed + AI 'why it matters'
- CVE watchlist with KEV & EPSS ranking
- Your stack + exposure matching
- Status board for 190+ SaaS & AI vendors
The same twenty minutes, twice.
- 08:40Open a dozen vendor status pages one at a time.
- 08:52Skim four newsletters, bookmark two things for later.
- 09:05Scroll the CVE feed, no idea which ones touch your stack.
- 09:20A user asks if Teams is down. Go and check again.
- 09:35Still no decision made. Later never comes.
- 08:40One brief: what's down, what's exploitable, what changed.
- 08:43Three items in the queue are yours. The rest say why they aren't.
- 08:48Patch one, schedule one, dismiss one. Queue is at zero.
- 08:50Slack already told the team about the outage.
- 08:52Done. The evidence log wrote itself.
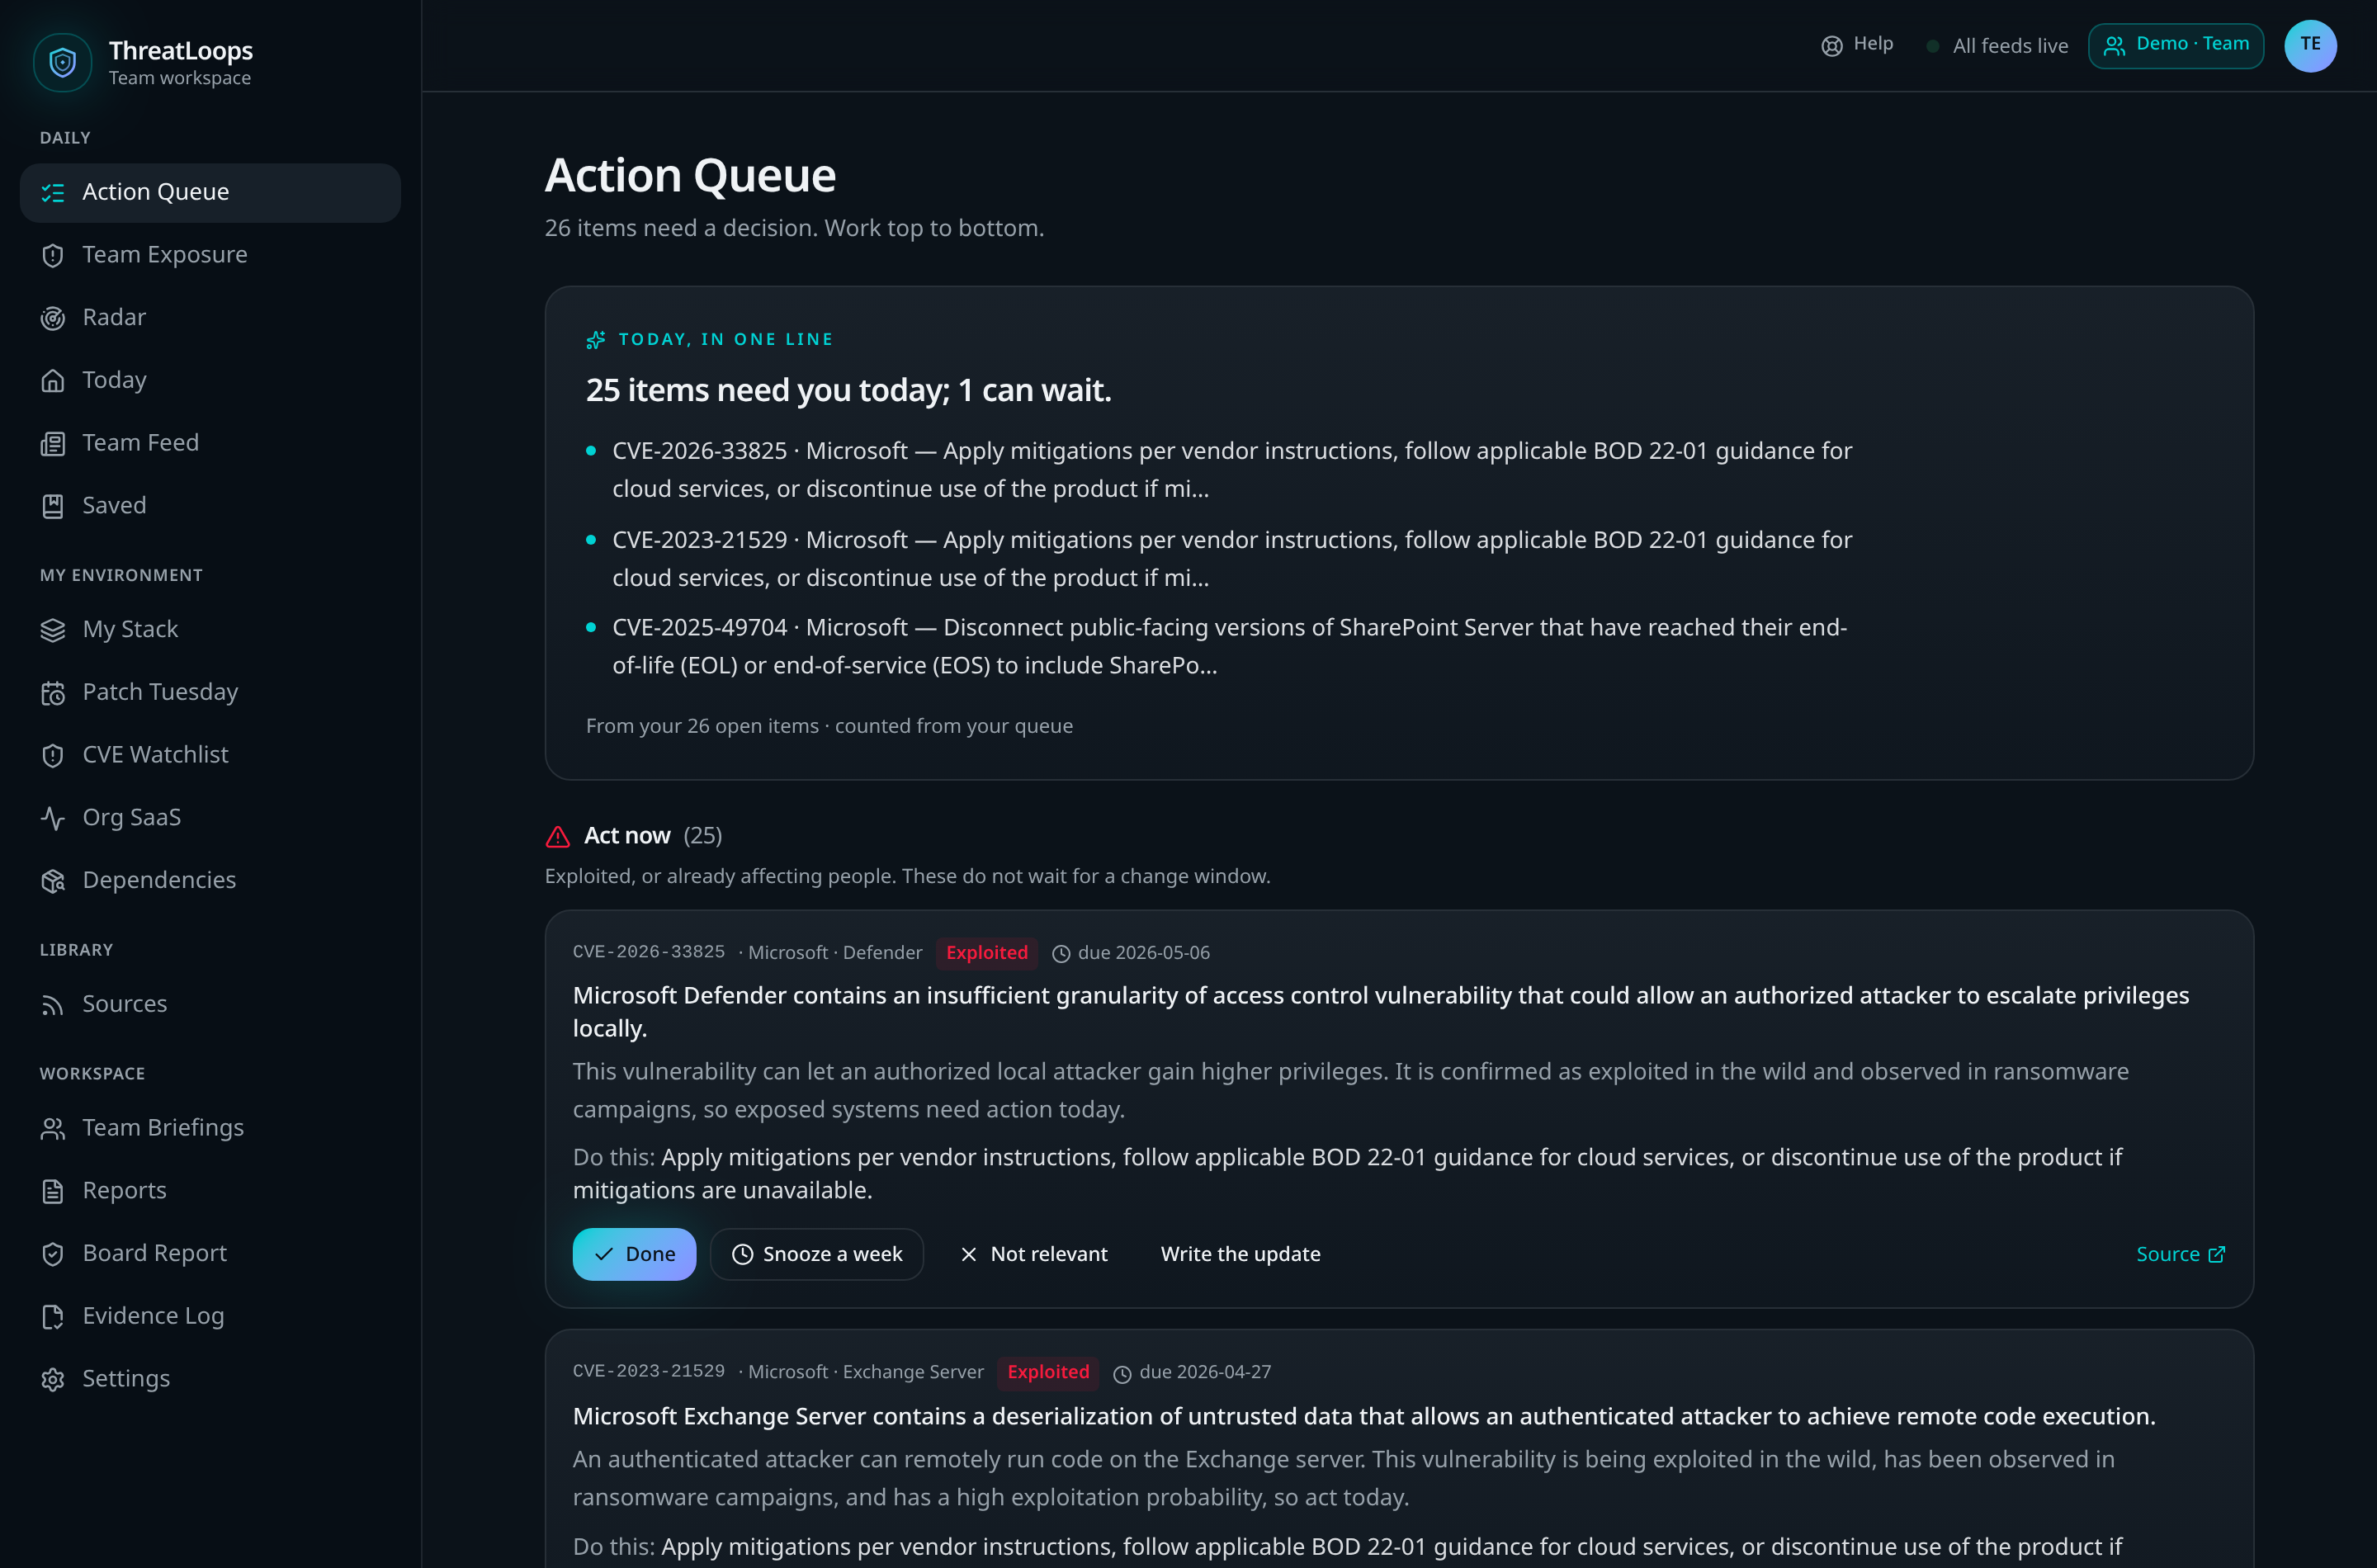
Every item gets one decision.
Do it, schedule it, or dismiss it. The list is built to reach zero.
Status monitoring is one feature, not the product.
Status-page tools tell you a vendor is down. They can't tell you a vulnerability in that same vendor is being exploited today. ThreatLoops does both — and starts at $19/mo against roughly $79/mo for status alone.
| Capability | ThreatLoops | Status-page tools |
|---|---|---|
| Live SaaS vendor status | Curated catalogue of the vendors SMB stacks actually run | Thousands of services monitored |
| Alerts to Slack, Teams or webhook | Yes, filtered to your stack and severity | Yes, plus help-desk and paging integrations |
| Shareable status board | Read-only link for your stack | Branded status pages with subscribers |
| CVE intelligence (KEV + EPSS) | Ranked by real-world exploitation, not CVSS alone | Not offered |
| Exposure matching to your stack | Every CVE, breach and advisory filtered to what you run | Not offered |
| Curated threat intelligence feed | 98 sources, deduped, with why-it-matters written for each | Not offered |
| Triage queue with verdicts | Act now / this week / ignore, with a reason | Not offered |
| Dependency (OSS) vulnerability scanning | Paste a lockfile, matched against OSV.dev | Not offered |
| MSP client reporting | Impact Radar plus co-branded client PDF reports | Multi-account views, no security reporting |
| Entry price | $19/mo | From about $79/mo |
Curated sources. No RSS-wrangling.
125 of those 194 vendors publish a machine-readable status feed and are polled automatically; the rest are tracked with a link to their status page.
Browse the full library30 days free. Then from $19/mo.
One exploited CVE you missed, or one outage you learned about from a user, costs more in incident hours than a year of this.
- Full threat feed + AI 'why it matters'
- CVE watchlist with KEV & EPSS ranking
- Your stack + exposure matching
- Everything in Solo
- 5 seats included ($9.80/seat), $8/seat after
- Shared in-app briefings + read tracking
- Everything in Team
- 10 client workspaces, $10/client after
- Per-client stacks and impact reports